Key takeaways
- The useful capability is not a model label; it is the ability to turn a defined task into a reviewable sequence of evidence, reasoning, tool calls and outputs.
- Industrial deployments should expose only the tools and data required for the approved workflow, with explicit permissions and a recorded action boundary.
- A strong model still needs evaluation against plant context, missing data, ambiguous instructions, unsafe requests, tool failures and manual fallback.
- Start with retrieval, drafting, triage and evidence preparation before allowing any action that changes an official record or operating condition.
- New capability announcements describe general technology direction, not a site-specific performance result, compliance outcome or production approval.
A new model capability is not a deployment plan
New frontier models are becoming better at carrying out multi-step tasks, working with large bodies of context, using approved tools and following explicit safety restrictions. Those capabilities can be useful to industrial teams, but they do not remove the need to define the decision, evidence boundary and accountable owner.
The practical question is not whether a model is “smart enough” for a factory, field operation, engineering project or regulated process. The practical question is whether a narrowly scoped workflow can be made inspectable, reversible and useful without giving the model authority it should not have.
This guide translates current public model-capability reporting into an industrial adoption pattern. It is not a benchmark, product recommendation, compliance statement or promise of a particular result.
What has changed in the capability layer
Recent frontier-model work is putting more emphasis on three capabilities that matter to enterprise workflows:
- Longer, more coherent task execution: - the system can maintain more context across a sequence instead of answering only one isolated question.
- Authorized tool use: - the system can call selected retrieval, calculation, workflow or record tools when the application explicitly grants access.
- Stronger restriction-following and monitoring: - model and system controls can be designed to detect unsafe requests, unauthorized actions or activity outside the approved scope.
These capabilities are useful building blocks. They are not evidence that a model understands an asset, procedure, process hazard or regulatory obligation without a carefully designed context layer.
A model may be able to read a maintenance history and draft a review summary. That does not make it the owner of the maintenance decision. It may be able to retrieve a controlled procedure and identify missing evidence. That does not make it the authority to approve a deviation. It may call a calculation or ticket-drafting tool. That does not make it safe to issue a control command.
Start with a bounded workflow
Choose a task that already has a responsible owner and a defined source of truth. Good first candidates include:
- preparing a review pack from approved maintenance records;
- finding the current procedure and identifying evidence gaps;
- classifying incoming documents before a person confirms routing;
- drafting a work request without submitting the official action;
- summarising an engineering change with links to the relevant records;
- triaging an inspection or operations queue into review categories.
Write the task as a contract:
- What question or decision does the workflow support?
- Which data sources may it read?
- Which tools may it call?
- What output may it create?
- Which actions are prohibited?
- Who reviews the result?
- What happens when evidence is missing or the system is unavailable?
The smaller the initial authority boundary, the easier it is to test whether the new capability is actually useful.
Give the model evidence, not just instructions
A general instruction such as “act as an industrial expert” is not an evidence design. The application should provide approved context with identity, revision, timestamp and permission state where those attributes matter.
For a procedure assistant, that may mean retrieving the current approved revision and showing why older material was excluded. For an engineering review, it may mean connecting a drawing, calculation, change record and acceptance criterion. For a maintenance summary, it may mean aligning the asset identity, event time, work history and relevant measurements.
The model should distinguish evidence from inference. A source record can support a statement; an inferred explanation should be labelled as a hypothesis; an unanswered question should remain unanswered. Do not fill an evidence gap with confident prose.
Make tool use narrow and visible
Tool use is valuable when it reduces repetitive work while leaving authority with the responsible process. It is risky when an application gives a general model broad write access to systems that affect safety, quality, production or official records.
Use an allowlist of tools with clear input and output contracts. Separate read tools from draft tools and draft tools from consequential actions. Put approval between the model’s recommendation and any action that changes an official record, releases material, changes an operating condition or affects a safety-critical workflow.
Log the request, retrieved evidence, tool call, returned data, model output, reviewer decision and final action. The log should make it possible to reconstruct what the system knew and what it was allowed to do at the time.
A denied tool call is also useful evidence. It shows that the workflow attempted an action outside its permission boundary and should be investigated rather than hidden.
Evaluate the complete system
A model capability announcement is not a site evaluation. Build a test set around the actual workflow and include cases that expose weak assumptions:
- normal requests with complete evidence;
- ambiguous requests where clarification is required;
- missing, stale or conflicting records;
- permissions that should prevent retrieval or action;
- tool timeout, malformed output and partial failure;
- instructions that ask for prohibited action;
- attempts to make the system ignore its operating boundary;
- new terminology, asset identifiers or document revisions;
- cases where the correct answer is to abstain or escalate.
Measure evidence retrieval, citation or record linkage, correct routing, refusal or escalation behaviour, tool-call accuracy, reviewer correction, latency, fallback success and the quality of the final work package. Do not collapse all of those into a single model score.
Repeat the evaluation after a model update, prompt change, retrieval-corpus change, tool change, permission change or workflow expansion. A new model can improve one capability while changing refusal behaviour, output structure or the kinds of errors reviewers see.
Keep industrial authority outside the model
A model can propose, summarise, classify, calculate or draft. The process owner decides whether the result is acceptable for the work at hand. This distinction matters most where the result affects people, product quality, equipment, production, environmental reporting or regulated records.
Design the interface so the reviewer can see the evidence, uncertainty, source revision, system version, tool calls and permitted options. Do not make the reviewer approve an opaque paragraph when the decision requires a traceable package.
Use explicit states such as draft, under review, approved, rejected, superseded and unavailable. Keep the official system of record authoritative. The AI layer should not create a parallel undocumented process that becomes impossible to audit when a person corrects it.
Apply safety controls to both users and system behaviour
Current frontier-model capability reports increasingly discuss safeguards against misuse and unauthorized actions. Industrial applications need the same two-sided view.
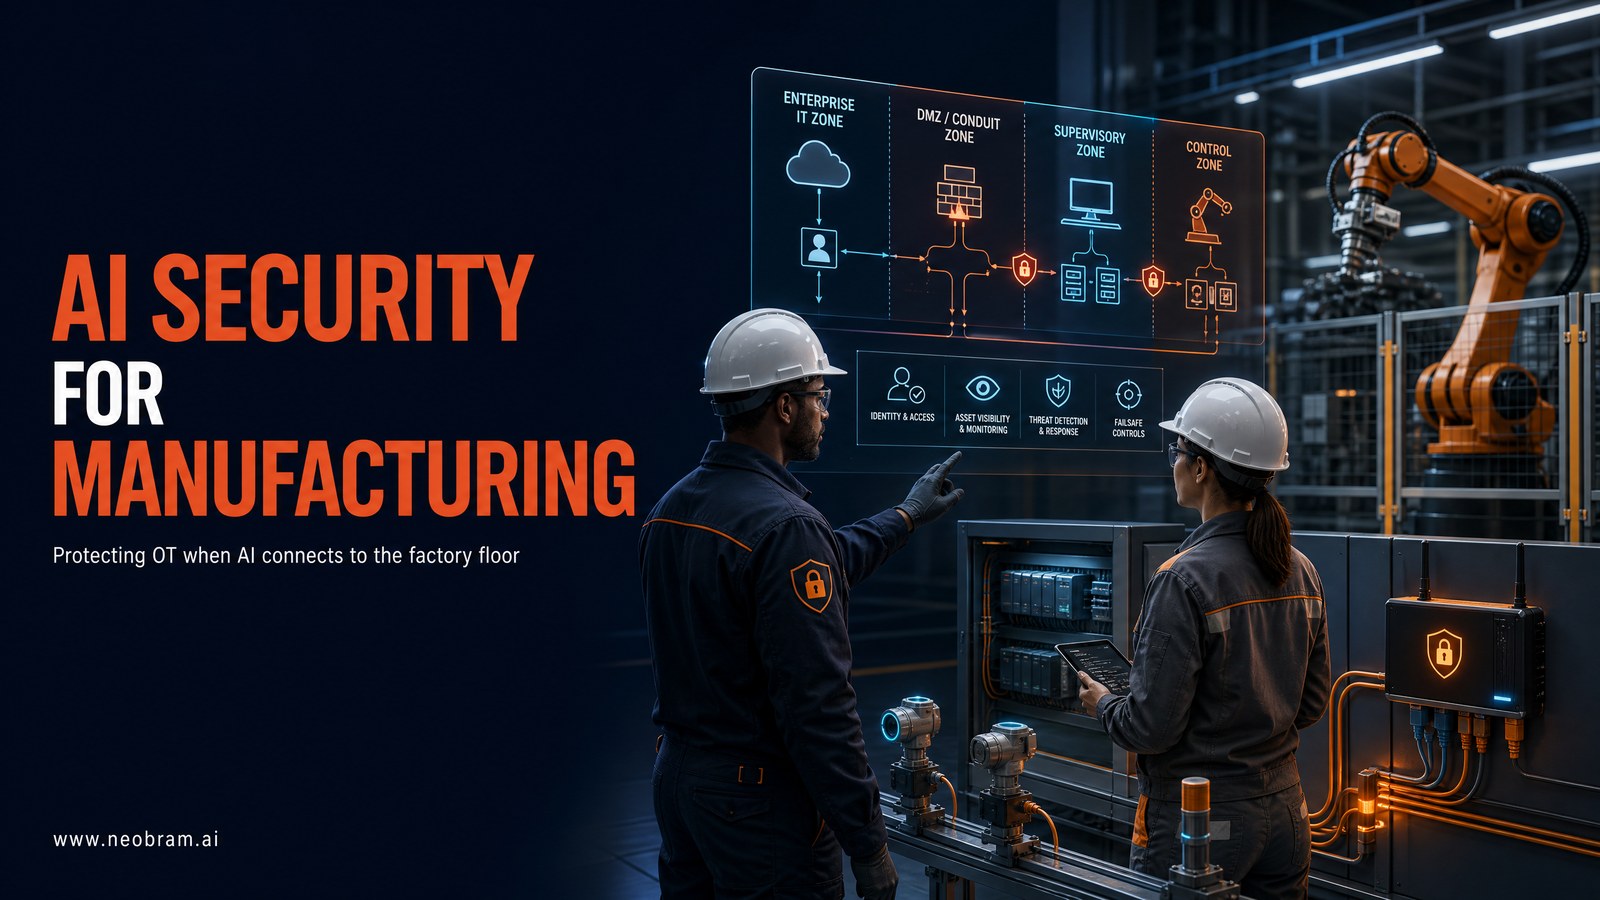
First, consider what an authorised or unauthorised user could ask the system to do. Limit data access, tool access, output destinations and action scope. Treat prompt content as untrusted input when it can influence tool calls or retrieved context.
Second, consider what the system might do incorrectly even when the user is not malicious. Monitor for attempts to leave the approved scope, unexpected tool sequences, repeated permission failures, fabricated evidence, unbounded retries and actions that do not match the workflow contract.
Layer controls. Model refusals are not a substitute for application permissions, network boundaries, approval gates, logging, rate limits, monitoring and a manual fallback. A safe industrial design assumes that one control can fail and makes the next control visible.
Use current model news without making a false promise
When a new model is released, treat the announcement as a signal to review the technology roadmap—not as evidence to rewrite a sales claim. Ask:
- Which capability is relevant to the workflow?
- Is the capability available in the deployment boundary the client requires?
- What data, tools and permissions would it need?
- Which evaluations demonstrate behaviour under the client’s conditions?
- What new failure modes or security concerns does the capability create?
- How can the team roll back to the existing process?
Keep public content neutral and evidence-led. Avoid claims that a new model will transform an industry, replace a team, promise compliance or deliver a specific operational result. The responsible message is that a capability may make a bounded workflow worth evaluating.
Plan delivery from India to international operations
A team delivering from India to international clients may help design, evaluate and operate an AI workflow, but the engagement must define the data and access boundary. Document where information is processed, who can access it, how support is authorised and logged, which tools are client-controlled and what the client receives at handover.
Contract-specific treatment is required for source code, configuration, prompts, retrieval assets, evaluation cases, deployment files, documentation, training and third-party dependencies. Do not imply that intellectual property rights, data transfer permissions, security outcomes or regulatory acceptance exist unless the reviewed contract and professional advice support the statement.
Cross-border delivery, data transfer, contracts, licences, security controls, tax, employment, privacy, intellectual property, export controls and sector obligations require client-specific review by qualified counsel and responsible professionals in the relevant jurisdictions. This article is a technology adoption guide, not legal, tax or regulatory advice.
A safe adoption sequence
Use a staged approach:
- Select one workflow: - choose a review, retrieval, drafting or triage task with a named owner.
- Map authority: - list data sources, tools, permissions, prohibited actions, approvals and fallback.
- Prepare evidence: - make identity, revision, timestamp and access state visible where relevant.
- Evaluate: - test normal, difficult, adversarial, missing-data and abstention cases.
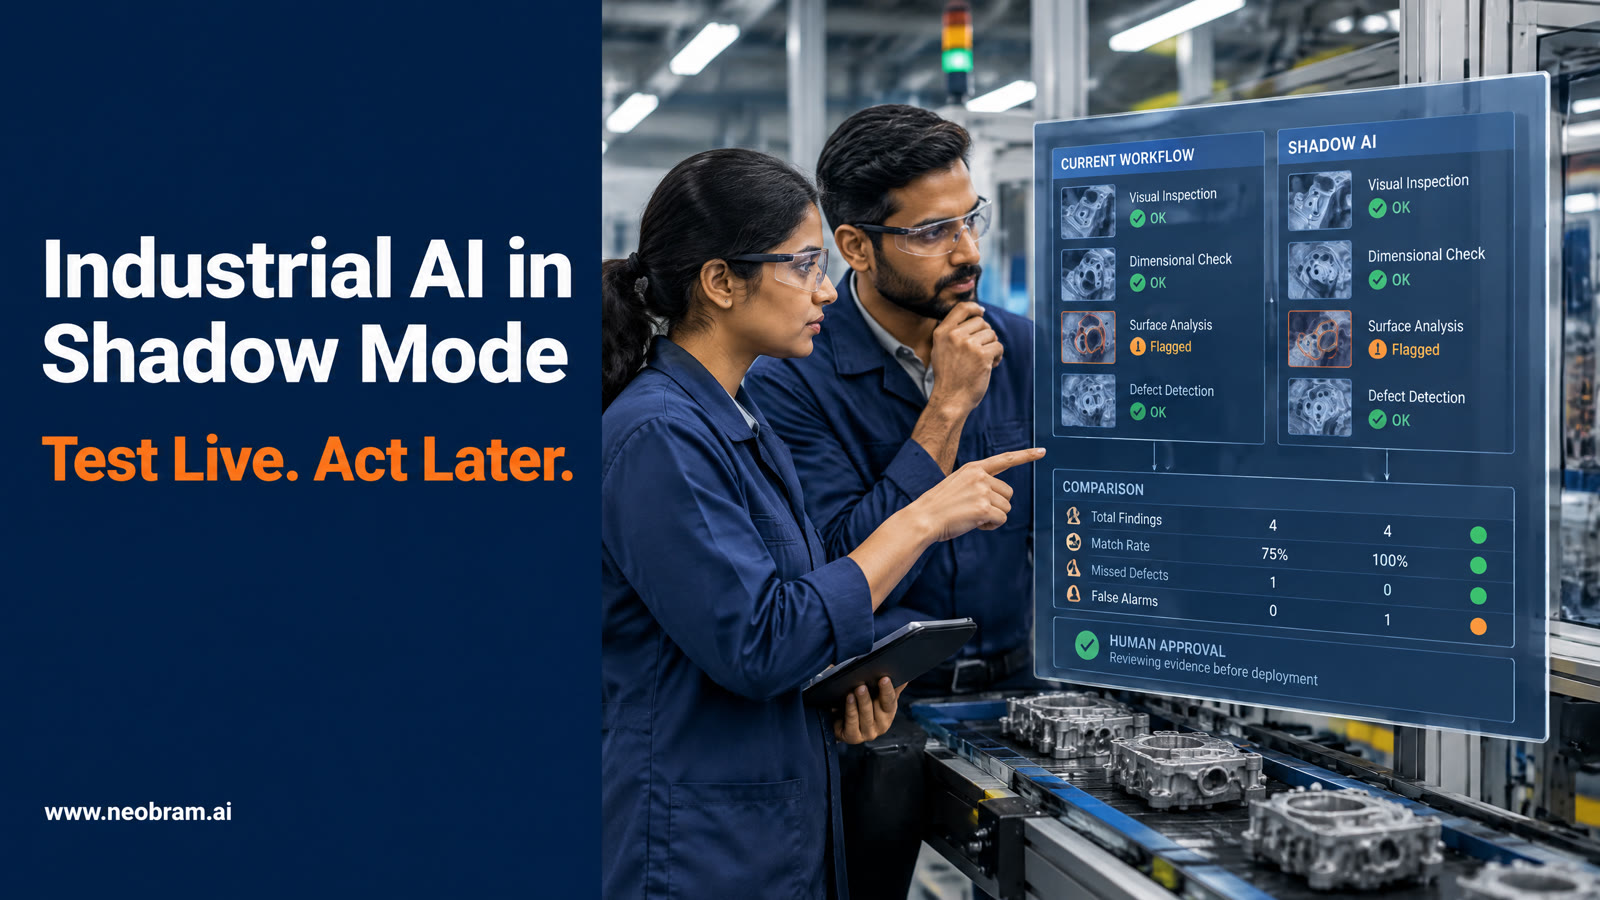
- Shadow: - run the new capability without changing the official decision or record.
- Release narrowly: - introduce read-only or draft-only use with logging and human review.
- Monitor: - inspect tool calls, refusals, corrections, drift, failures and unauthorized attempts.
- Expand by evidence: - revisit the evaluation and authority boundary before adding data, tools or actions.
This approach lets an industrial team learn what a new model can contribute without confusing capability with permission.
The practical takeaway
New frontier models can make industrial knowledge work more capable: they may handle longer tasks, connect evidence across records, use approved tools and follow stronger restrictions. The safe advantage comes from putting those capabilities inside a bounded workflow.
Start with one decision. Give the system authoritative context. Make tool access narrow. Test refusal and fallback. Keep people responsible for consequential decisions. Log what the system saw, did and was allowed to do. Treat every model update as a new evaluation event.
A new model is worth adopting when it makes accountable work clearer and more useful—not when it makes authority harder to find.